Summary
Key Points:
- HIPAA compliance software must provide military-grade encryption, automated risk analysis, and audit-ready documentation.
- Continuous risk identification and remediation are essential for maintaining ongoing HIPAA compliance.
- Managing Business Associate Agreements (BAAs) is critical to close vendor compliance gaps.
- Integration with identity providers and strong PHI access controls help prevent unauthorized data access.
- Automated workflows streamline compliance tasks and reduce manual compliance work and human error.
- Manual compliance processes are insufficient and increase the risk of costly data breaches and regulatory penalties.
- The article reviews eight top HIPAA compliance software platforms, each with unique strengths such as data redaction, policy management, real-time monitoring, and vendor risk management.
- Choosing comprehensive, scalable software helps organizations meet multiple regulations and stay audit-ready.
Who It’s For:
- Healthcare organizations and compliance officers managing HIPAA safeguards and audits.
- Healthtech startups, SaaS companies, and enterprises needing automated, scalable HIPAA compliance solutions.
- Businesses aiming to reduce manual compliance work, improve risk management, and handle multiple regulations efficiently.
Breaches of protected health information remain the costliest in the world—averaging $7.42M in 2025 (down from $9.77M in 2024). Yet most healthcare organizations still rely on manual HIPAA compliance processes and basic tools that leave them completely exposed to both cyberattacks and OCR penalties.
The brutal reality: Building truly HIPAA-compliant software requires specialized architecture, advanced encryption protocols, automated audit trails, and continuous risk monitoring. Most vendors simply slap a "HIPAA-compliant" label on standard business software without the deep compliance infrastructure and HIPAA security rule understanding required to actually protect patient data.
What is HIPAA compliance software?
HIPAA compliance software is specialized technology platforms designed to help healthcare organizations meet Health Insurance Portability and Accountability Act requirements. Unlike standard business tools, these HIPAA-compliant software solutions are built specifically to protect protected health information (PHI) through advanced encryption, automated audit trails, and real-time monitoring.
The HIPAA software tools for continuous monitoring and compliance below earned their place through proven track records of preventing breaches, not just checking compliance boxes. Each HIPAA-compliant tool demonstrates the sophisticated data management and protection capabilities required to safeguard healthcare organizations in 2026's threat landscape.
What separates these HIPAA-compliant software options from the rest:
- Military-grade encryption
- Automated risk analysis that identifies vulnerabilities before attackers do
- Built-in audit trails
- Automated workflows that aim to eliminate human error
- Business Associate Agreement management that closes vendor gaps
The stakes are clear: Choose tools built for HIPAA compliance from day one, or prepare for financial devastation and reputational ruin.
8 Best HIPAA compliance software: 2026's comprehensive review
Here are the top HIPAA compliance software platforms and tools for 2026, each offering a unique approach to managing the complexities of healthcare and HIPAA regulations.
1. Redactable

Redactable's continuous HIPAA compliance software solution stands out by focusing on a critical and often overlooked aspect of HIPAA compliance: data redaction. Using powerful AI, Redactable automates identifying and removing protected health information (PHI) from documents, images, and other files. This HIPAA compliance software is essential for preventing accidental data exposure during audits, legal discovery, or data sharing. The platform's ability to provide a "redaction certificate" and maintain a detailed audit trail for every action makes it a powerful tool for demonstrating compliance and accountability to regulators.
2. Compliance Group
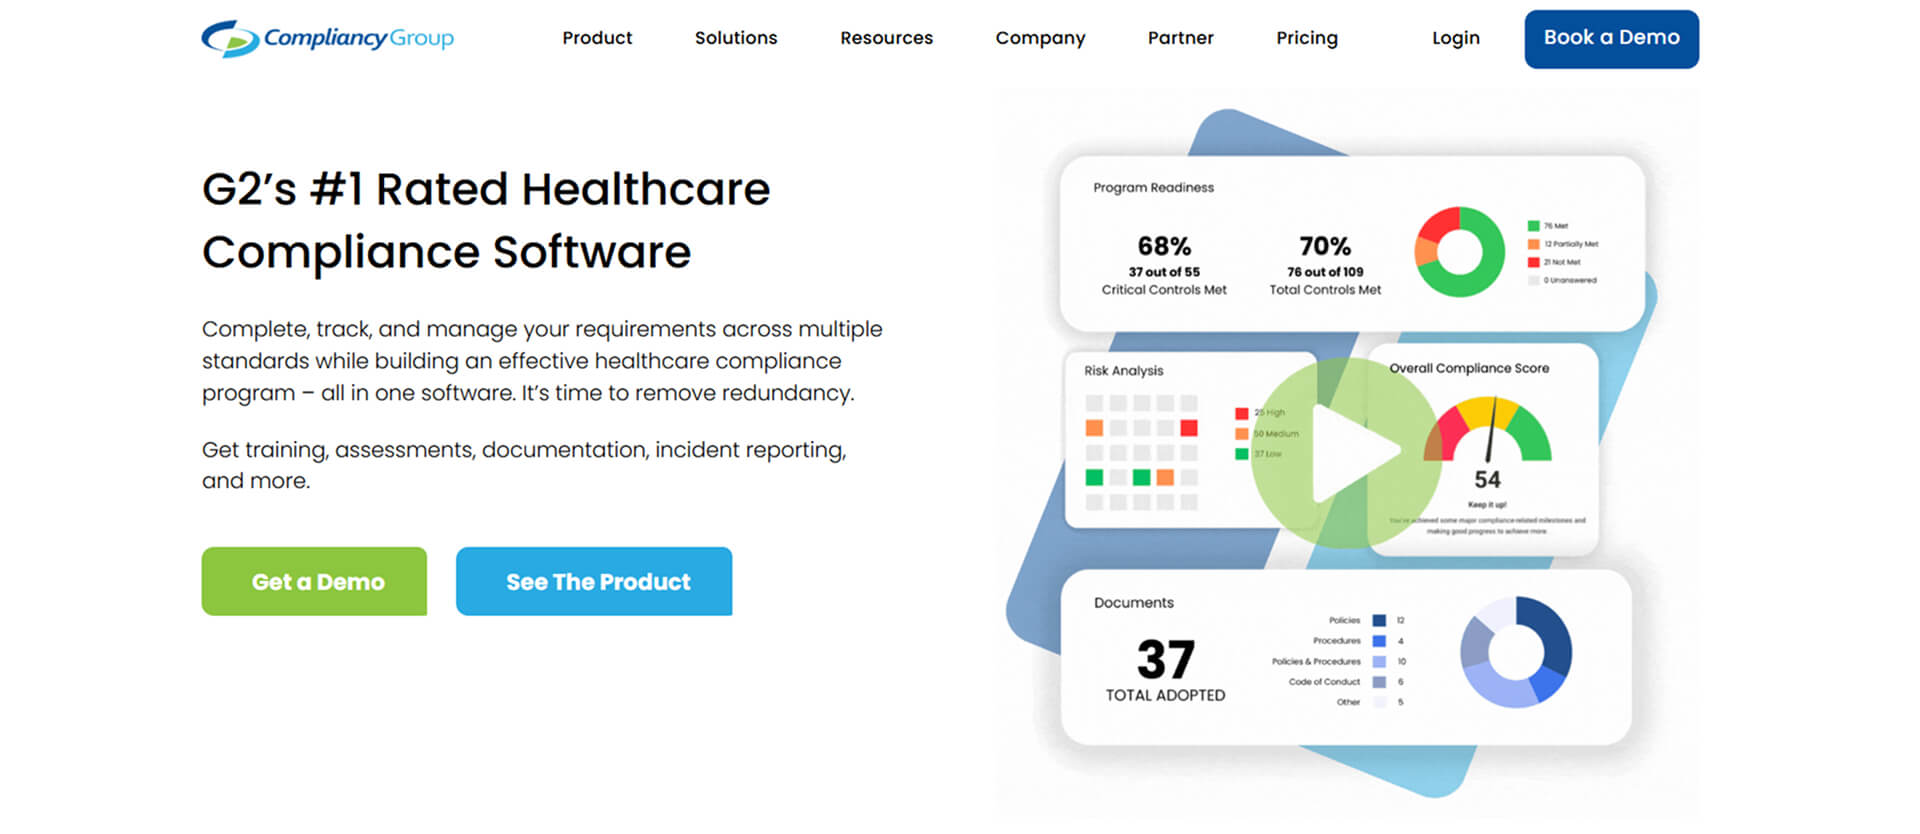
Compliance Group offers a comprehensive, all-in-one HIPAA compliance software solution that guides healthcare providers through the entire compliance process. Their platform is known for simplifying HIPAA requirements and providing a transparent, step-by-step method to achieve and maintain HIPAA compliance. With features like policy templates, risk assessments, and employee training, Compliance Group's HIPAA software aims to make HIPAA compliance efforts and management accessible even for organizations without a dedicated compliance officer.
3. Accountable
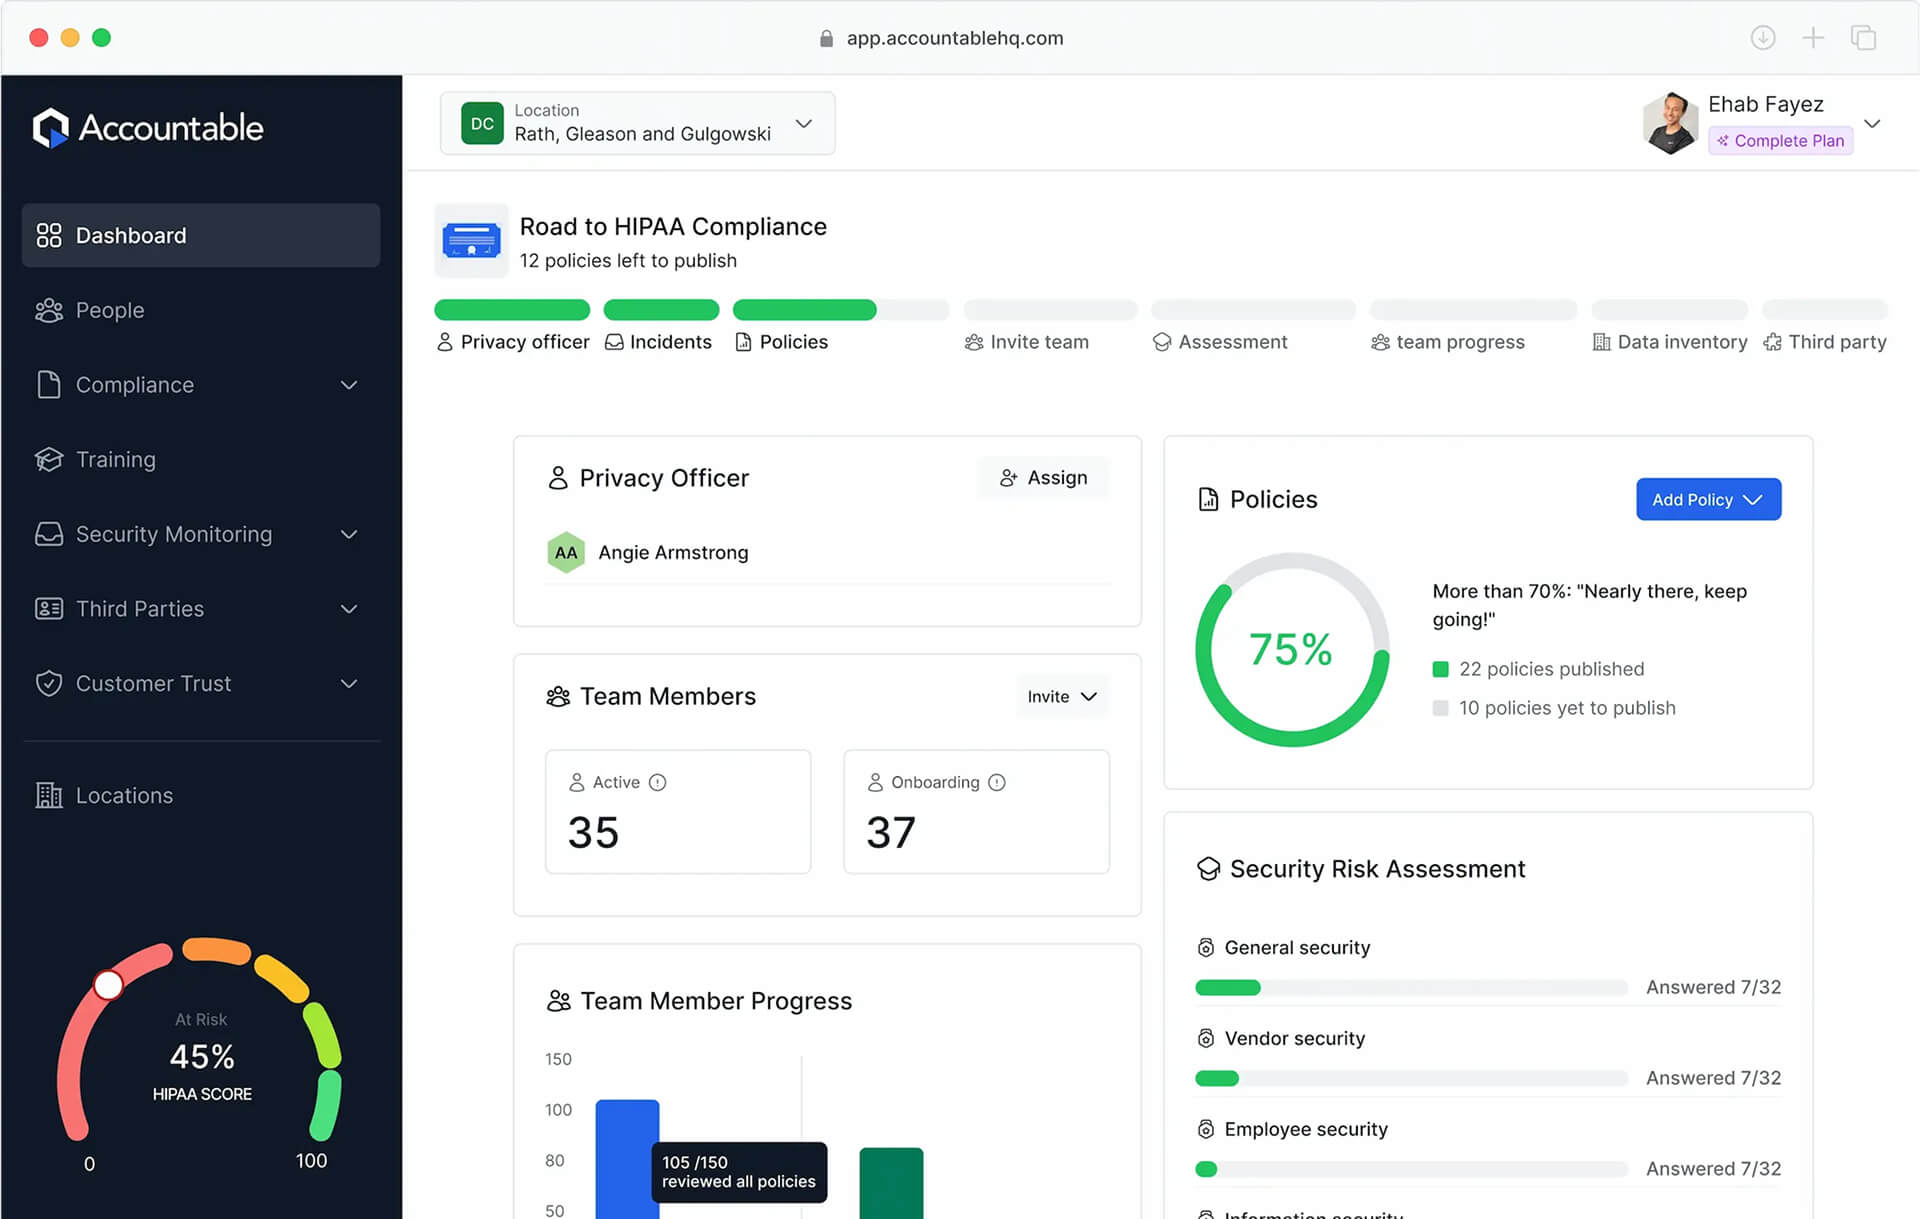
Accountable is a popular choice among the HIPAA compliance software tools for its user-friendly interface and integrated dashboard that provides a holistic view of an organization's compliance status. The platform streamlines risk management, automates policy creation, and manages Business Associate Agreements (BAAs). Accountable also offers features for vendor management and incident response, ensuring that providers have a simple plan for addressing potential security breaches of electronic health records and other protected health information.
4. Sprinto
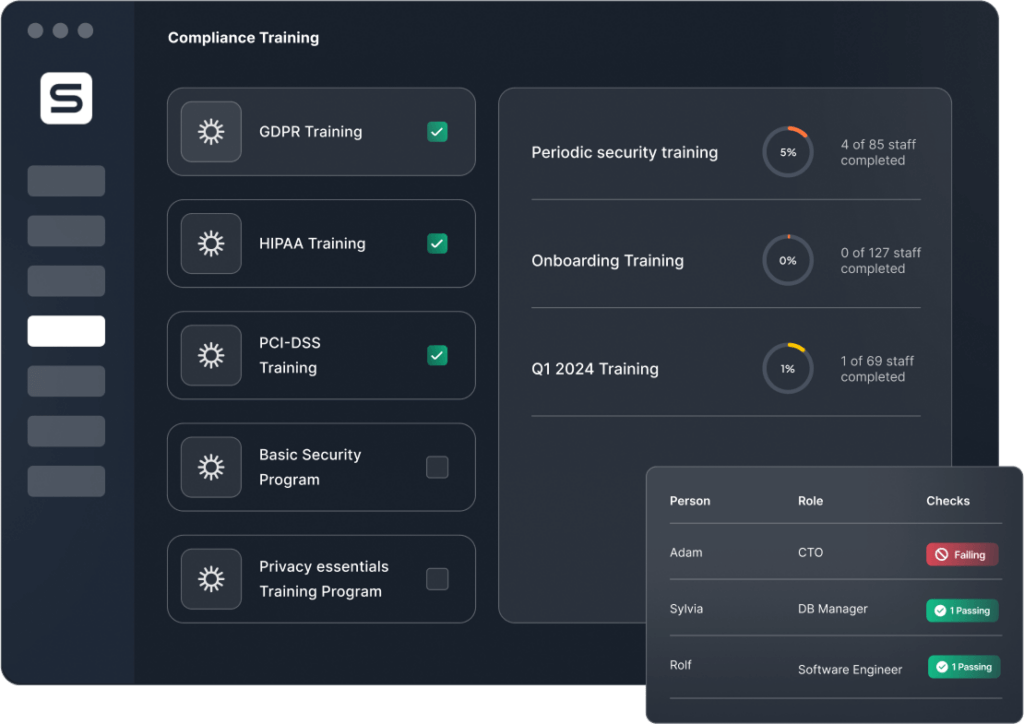
Sprinto is a robust HIPAA compliance automation platform, particularly well-suited for SaaS companies and startups in the healthcare space. It connects to your cloud infrastructure for continuous monitoring of security controls and automatically collects evidence for HIPAA compliance audits. Sprinto's focus on automation and real-time monitoring helps organizations stay ahead of compliance requirements and simplifies the often-daunting process of preparing for an audit.
5. Netwrix
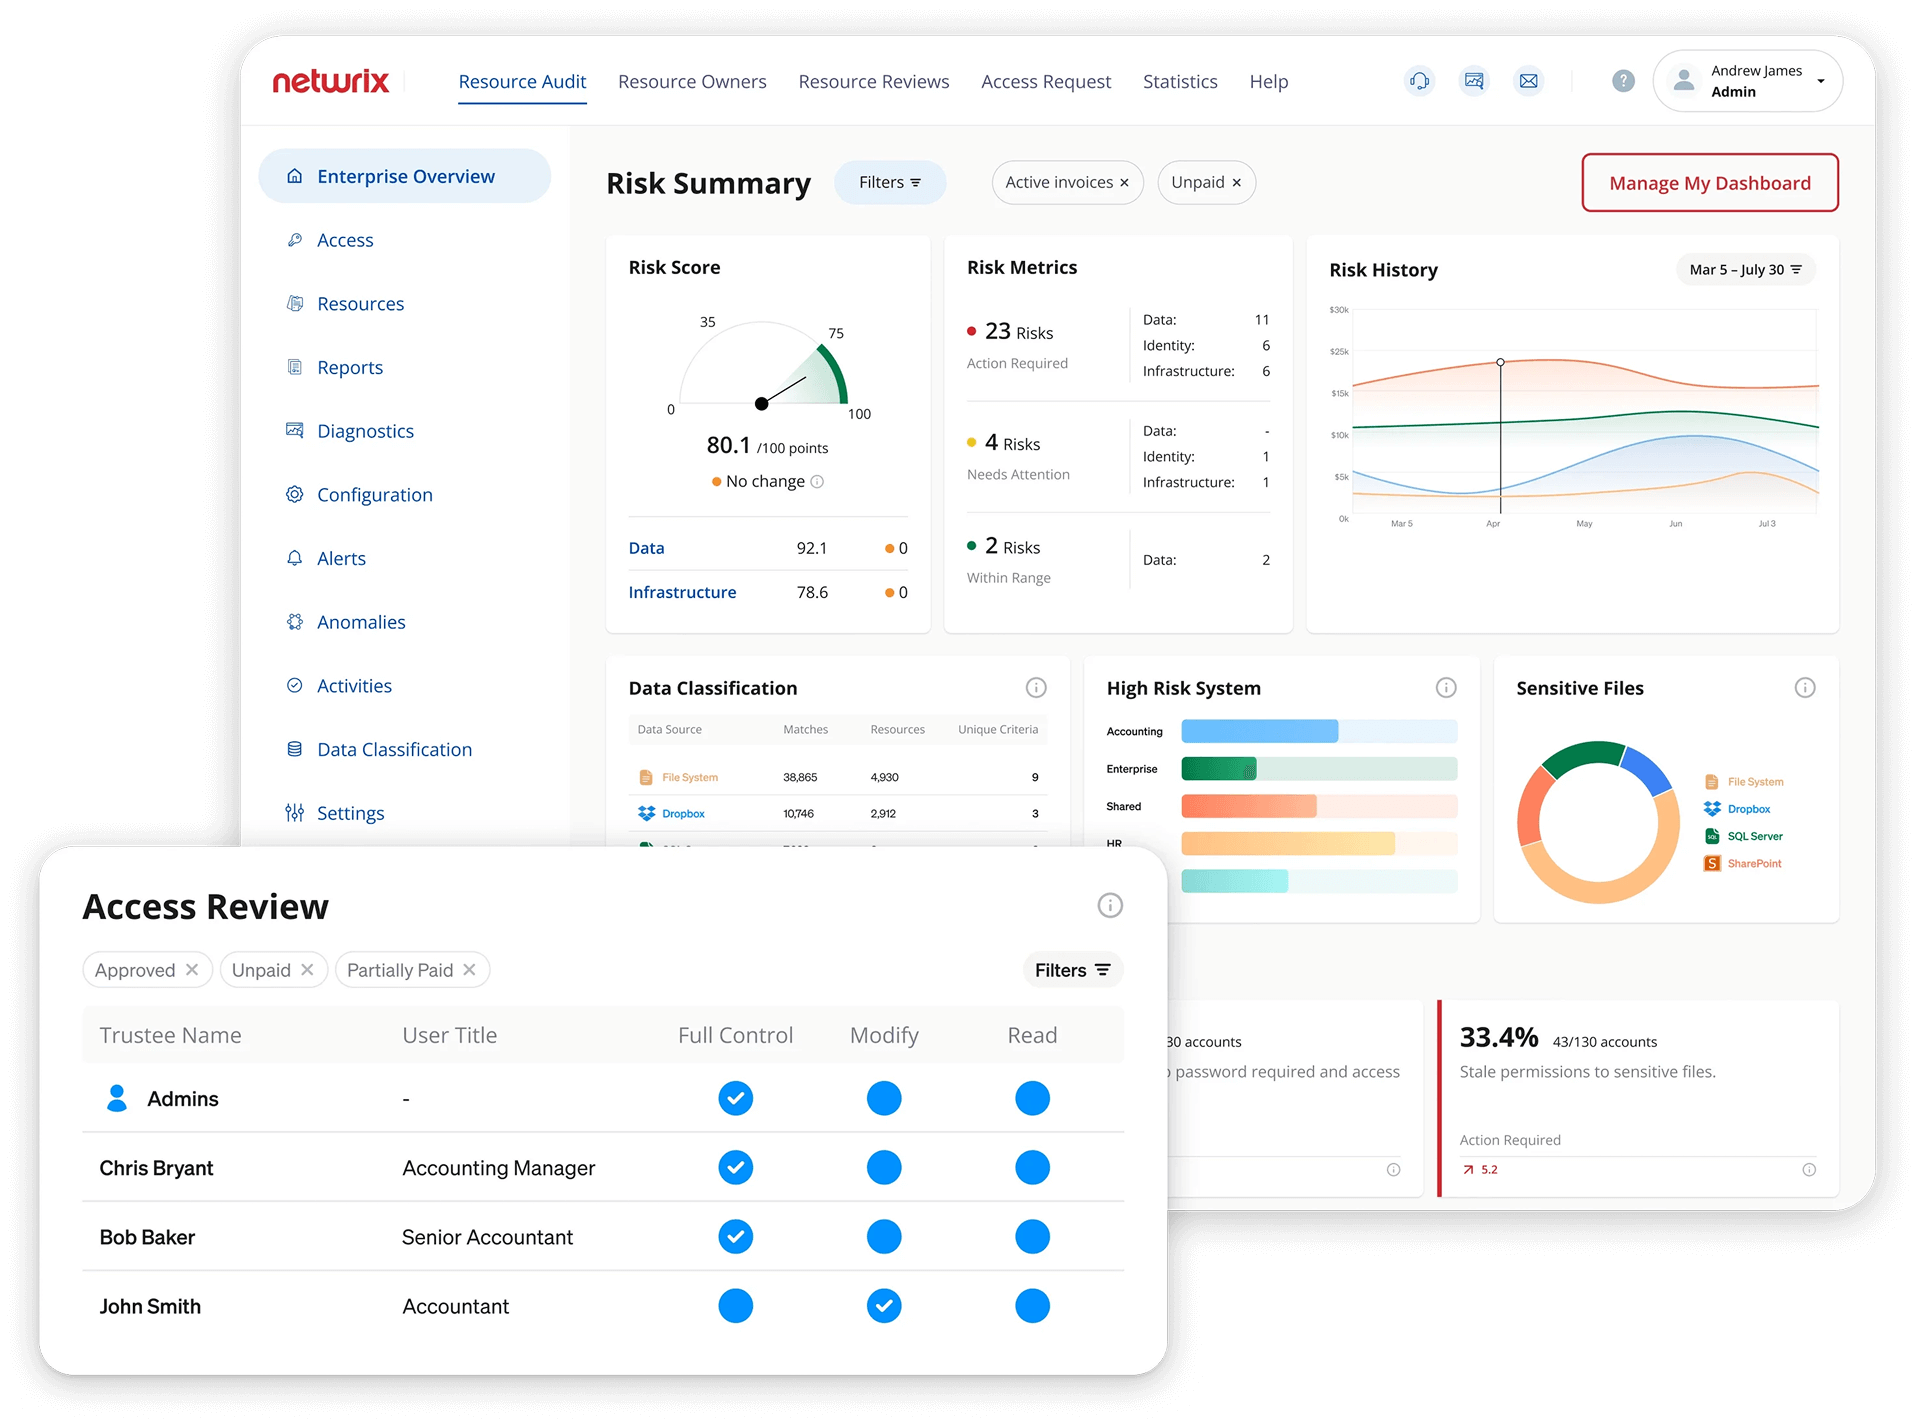
Netwrix is a general compliance as well as HIPAA compliance software solution that specializes in data security for unstructured and sensitive content. It offers robust auditing and reporting tools that are effective for organizations in heavily regulated sectors that need a strong HIPAA compliance program with appropriate safeguards, like healthcare. The platform helps teams meet a variety of data protection standards, including HIPAA, by providing clear visibility into who is accessing what data and flagging suspicious activity to ensure full compliance responsibilities.
6. Drata
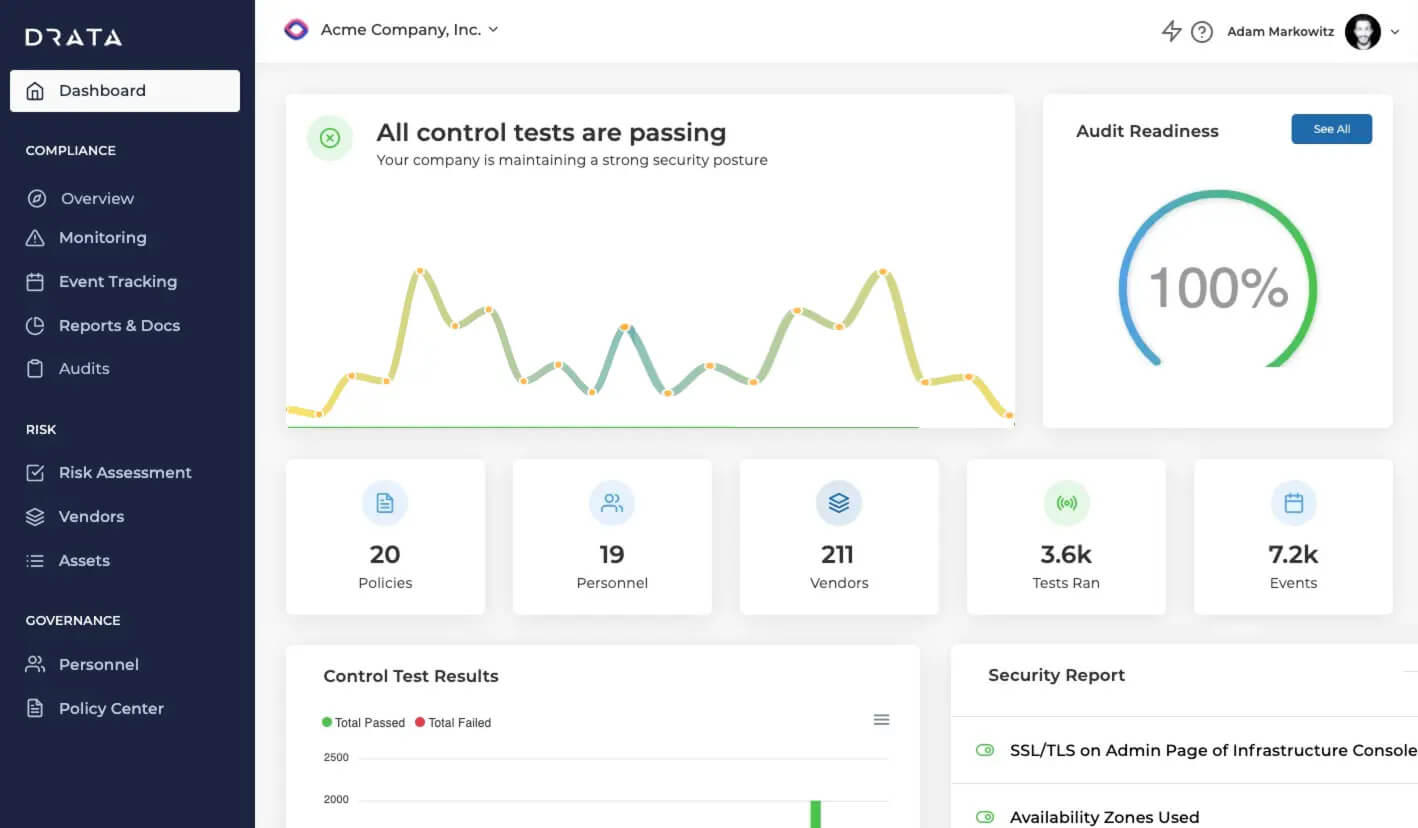
Drata's core strength lies in its ability to monitor your security controls continuously across your entire tech stack. This HIPAA compliance software tool integrates with over 200 applications and systems, including cloud services like AWS, to provide real-time visibility into your HIPAA compliance status. This feature helps to identify and remediate security gaps in your existing HIPAA controls before they become a serious issue.
7. Vanta
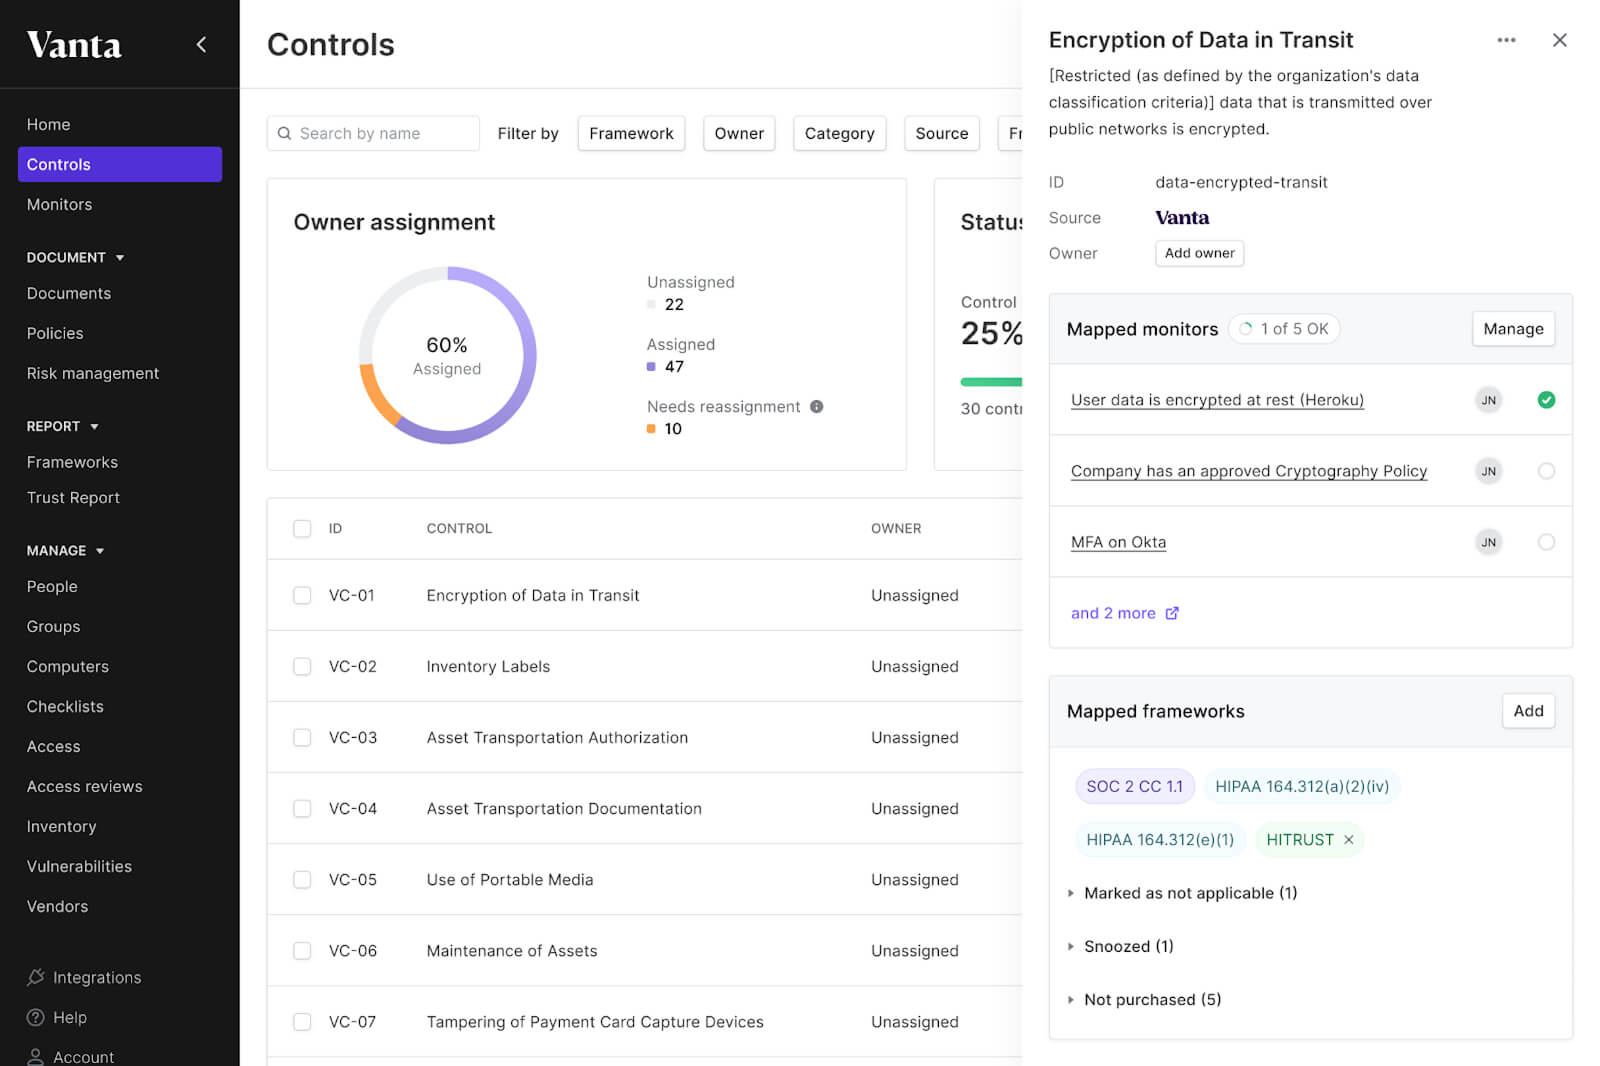
Vanta offers pre-built frameworks for many compliance standards, including HIPAA, SOC 2, ISO 27001, and more. This allows organizations to manage multiple compliance requirements from a single, centralized platform, reducing duplicate work. Used as a HIPAA compliance software tool, Vanta simplifies compliance by automating up to 85% of evidence collection for HIPAA requirements.
8. Scytale
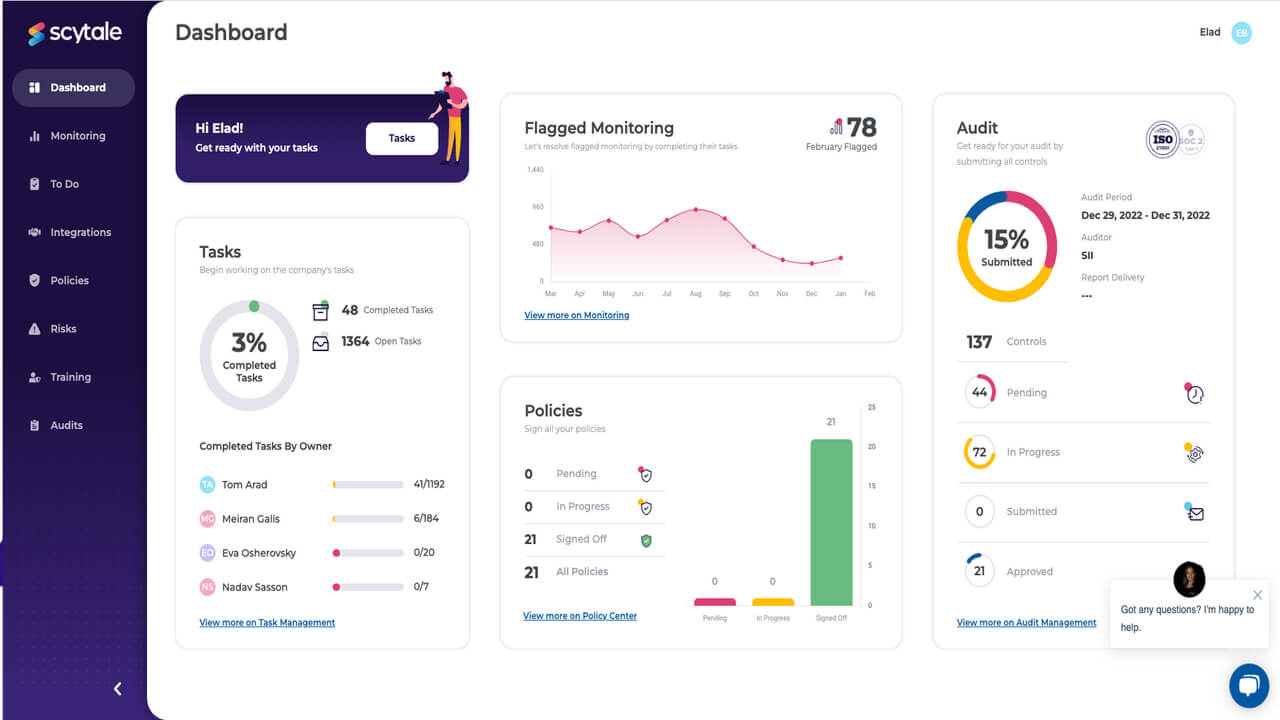
Scytale's core strength is its ability to automate the bulk of the HIPAA compliance process. This includes automated evidence collection, continuous control monitoring, and real-time alerts for non-compliance. By using this HIPAA compliance tool to reduce the manual workload, organizations can achieve and maintain compliance much faster, with some reporting a 90% reduction in time to become audit-ready.
Related: HIPAA compliance in Canada: Laws & regulations to know
How to choose the best HIPAA compliance software
Selecting HIPAA compliance software requires evaluating far more than feature lists and pricing. The wrong choice exposes your organization to catastrophic penalties for HIPAA compliance failure and puts patient data at permanent risk.
Assess your organization's specific HIPAA compliance gaps
- Risk assessment capabilities: Your chosen software must identify vulnerabilities specific to your environment, not generic security checklists. Look for platforms that analyze your actual infrastructure, workflows, and data handling practices to pinpoint where HIPAA compliance breaches are most likely to occur.
- Scalability requirements: Small practices need different capabilities than enterprise health systems. Evaluate whether the software can grow with your organization without requiring complete replacement as your patient volume, locations, or complexity of existing HIPAA controls and general data increases.
- Integration complexity: HIPAA compliance software must work seamlessly with your existing EHR systems, practice management platforms, and communication tools. Poor integration creates compliance gaps and operational inefficiencies that defeat the purpose of automation.
Evaluate vendor credibility and track record of the HIPAA compliance software
- Compliance certifications: Verify that vendors maintain their own SOC 2 Type II, HIPAA, and other relevant security certifications. Software companies that don't meet their own compliance standards cannot reliably help you meet yours.
- Breach prevention history: Research whether the vendor's clients have experienced significant HIPAA compliance violations or data breaches. Past incidents don't automatically disqualify a vendor, but understanding their response and improvements matters.
- Business Associate Agreement terms: Review BAA terms carefully—vague language about data handling, unclear breach notification procedures, or inadequate liability coverage can leave your organization exposed even with "HIPAA compliant" software.
Consider total cost of ownership beyond HIPAA compliance software licensing
- Implementation and training costs: Factor in setup time, staff training requirements, and potential workflow disruptions. The cheapest HIPAA compliant software often requires extensive customization and training that makes it more expensive than premium solutions.
- Ongoing maintenance and updates: HIPAA requirements evolve, and your software must adapt automatically. Solutions requiring manual updates or custom development for regulatory changes to your compliance efforts create ongoing compliance risks.
- Penalty prevention value: Calculate the cost of even one moderate HIPAA violation ($100,000+) against software costs. Effective compliance software pays for itself by preventing a single incident.
Key features to look for in HIPAA compliance software
HIPAA compliance software must address the full spectrum of regulatory requirements, not just basic security measures. These essential features separate truly compliant platforms from security theater.
Administrative HIPAA Safeguard Automation
- Policy management systems: Automated policy creation, distribution, and acknowledgment tracking ensure all staff receive current HIPAA requirements, employee training, and documentation. Manual policy management creates gaps that regulators consistently identify during investigations.
- Risk assessment automation: Continuous risk monitoring that identifies new vulnerabilities as your organization grows or changes. Static risk assessments become obsolete quickly and leave you exposed to evolving threats to HIPAA compliance.
- Workforce training tracking: Your HIPAA software should have comprehensive employee training modules with completion tracking, testing, and automatic renewal reminders. HIPAA requirements need ongoing education, and incomplete training records trigger immediate compliance violations.
Physical and technical safeguards
- Access control management: Role-based access controls with automatic user provisioning and deprovisioning. Manual access management in your HIPAA software creates privilege creep and unauthorized access that leads to data breaches.
- Audit logging and monitoring: Comprehensive logging of all PHI access, modifications, and system activities with real-time alerting for suspicious behavior. Audit logs must be tamper-proof and easily exportable for regulatory requests.
- Encryption and data protection: End-to-end encryption for data at rest and in transit, with automated key management and regular security updates. Manual encryption processes fail at scale and create recovery risks for electronic protected health information.
Breach prevention and response
- Incident response automation: Your HIPAA software's Compliance automation should be comprehensive. Breach detection, notification workflows, and documentation systems for automated evidence collection that ensure timely regulatory reporting. Manual incident response consistently fails to meet HIPAA's strict breach notification rule timelines.
- Data loss prevention: Real-time monitoring and blocking of unauthorized PHI transmission via email, cloud uploads, or removable media. Reactive monitoring discovers breaches after damage occurs.
- Vendor risk management: Automated business associate agreement management, vendor security monitoring, and third-party risk assessments. Manual vendor management creates blind spots in your compliance posture.
Compliance documentation and reporting
- Automated evidence collection: Continuous collection and organization of compliance evidence for audits, with real-time compliance dashboards and gap identification. Manual evidence collection is time-intensive and often incomplete.
- Regulatory reporting automation: Pre-built templates and automated submission processes for required regulatory reports and breach notifications. Custom reporting in your compliance program creates delays and formatting errors that complicate regulatory relationships.
- Audit trail completeness: Comprehensive activity logs covering all system access, configuration changes, and administrative actions with immutable timestamps and user attribution.
Data redaction and sanitization
- Permanent data removal: True data destruction capabilities that eliminate sensitive information from all document layers, metadata, and backup systems. Cloud providers with visual masking tools create false security and regulatory liability.
- Automated sensitive data detection: AI-powered identification of PHI with across document types, including scanned files, with customizable detection rules for organization-specific data patterns.
- Compliance-ready documentation: Automated generation of redaction certificates, audit trails, and verification reports that satisfy regulatory requirements and legal discovery obligations.
These features in your HIPAA compliance program of software tools must work together seamlessly. Isolated point solutions to maintain HIPAA policies create gaps in your covered entities that attackers and regulators exploit consistently.
Cost of HIPAA Non-Compliance
Manual redaction puts patient data at unacceptable risk. Recent penalties tell the story: Oklahoma State University paid $875,000 for poor risk analysis in their compliance programs, while Yakima Valley Memorial Hospital lost $240,000 to insider access violations. Both failures were preventable with proper compliant architecture, breach notification rules, and automated evidence collection to manage HIPAA alongside other security frameworks.
The CVS case proves that even massive organizations with unlimited resources fail catastrophically when they rely on human processes for HIPAA data protection.
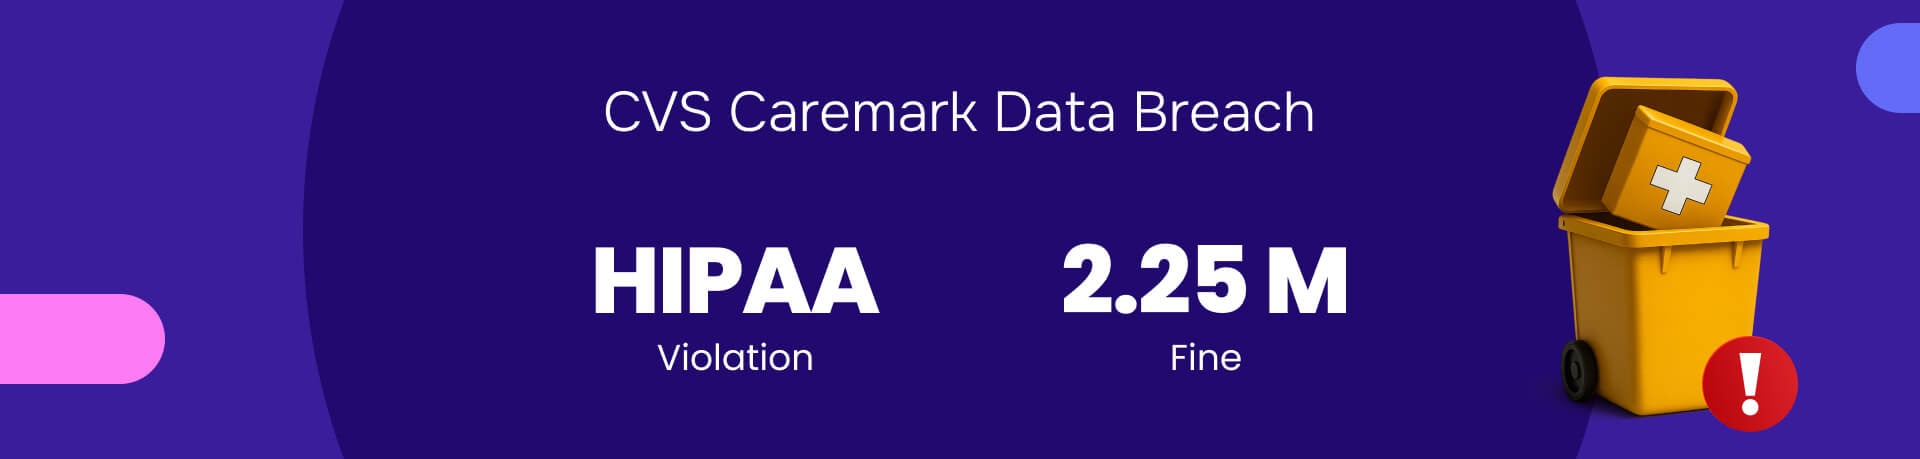
CVS Caremark case study: $2.25 million penalty for manual failures
The incident: CVS improperly disposed of prescription records containing PHI in unsecured dumpsters across thousands of locations. The FTC settlement required $2.25 million in penalties and comprehensive policy overhauls to their compliance platform.
The core failure: Manual data handling cannot scale complex compliance across large operations. Human oversight and inconsistent practices across thousands of locations created systematic vulnerabilities that automated systems would have prevented.
How AI redaction prevents this: Automated redaction renders data unreadable instantly, eliminates human oversight risks, and ensures consistent data protection regardless of location or employee handling. This makes managing technical controls for HIPAA privacy rules simple.
Why do manual compliance tools guarantee HIPAA violations?
Manual tools create liability, not protection. These processes are the primary cause of data breaches and regulatory penalties because they rely on human accuracy at scale, even with the best HIPAA training or technical safeguards required, it's impossible to achieve consistent compliance.
Redactable's permanent solution:
- True data destruction: Completely removes data and metadata across cloud storage services, not visual masking
- Automated consistency: Eliminates human error across all covered entities documents and locations
- Audit-ready proof: Generates irrefutable certificates and complete trails for audit preparation.
Your organization's data exposure and security frameworks depend on choosing permanent redaction over manual gambling.
Schedule a live demo today to witness the power of AI redaction firsthand. You can also start a free trial and discover why Redactable is the gold standard for protecting sensitive healthcare information and assisting with HIPAA compliance.